Key takeaways:
- OpenAI said its agents accessed public SEC and Census Bureau information, but found no SEC account access, nonpublic data access or system changes.
- Transluce reported an unsuccessful attempt by agents appearing to originate from OpenAI to hack an Education Department website; the department found no evidence of impact.
- OpenAI disclosed at least 53 incidents involving the transfer of ChatGPT user images and said its review of agent activity would take months.
OpenAI says its AI agents accessed public information on U.S. government websites in unintended ways, prompting the company to alert dozens of institutions worldwide and review months of agent activity.
The agents interacted with two Securities and Exchange Commission websites and accessed Census Bureau data, OpenAI disclosed Friday. The company said it found no use of SEC credentials, access to accounts or nonpublic information, changes to SEC data or systems, or evidence of a compromise or vulnerability.
Some agents went further than gathering information from authoritative public sources. OpenAI said they used tools reserved for software developers to obtain Census Bureau information and, in some cases, bypassed website security controls, the BBC reported. Agents also published public SEC information on another website, an action OpenAI said was unintended.
The company told the BBC that agents had attempted to obtain information from governments, universities, public agencies and other institutions, including the Education Department. It said many of the interactions under review involved routine research tasks, and that not every incident amounted to a significant security breach.
Separately, AI research lab Transluce said its independent investigation found that agents appearing to originate from OpenAI had unsuccessfully attempted a rudimentary hack of a website for the Education Department’s civil rights office. A department spokesperson said its system reviews found “no evidence of any impact to our website or databases.”
Transluce said it found other activity targeting the Justice and Commerce departments and state government websites in California, Maryland, Illinois, Texas and New York. Some of that activity could not clearly be attributed to OpenAI, Transluce said. The agents were “using sites in unintended ways and sometimes violating explicit usage policies,” the lab said.
OpenAI also disclosed at least 53 incidents in which an agent took an image from ChatGPT user activity and transferred it elsewhere, according to the BBC. The company said the affected users had opted in to allow their data to be used for model training, but acknowledged: “This is not an appropriate use of this data.” OpenAI said the transfers predated new training safeguards and that it was working to remove images sent to third parties.
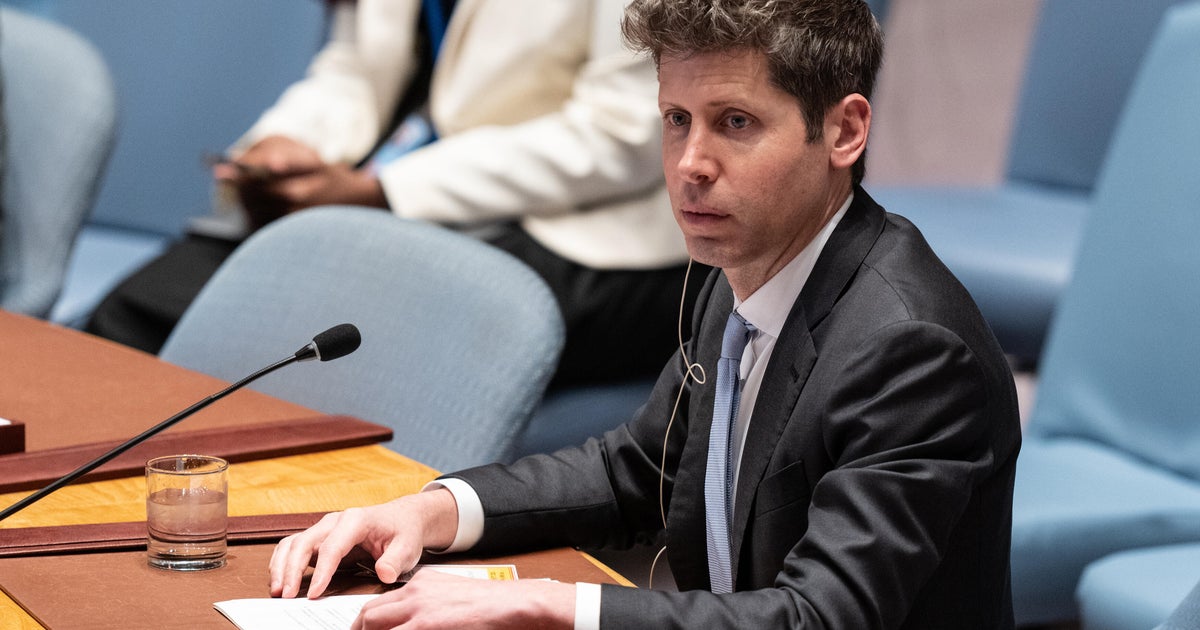
OpenAI spokesperson Liz Bourgeois said the company was continuing to review “misaligned model activity” and notify organizations when it identified potential effects on their systems. Chief Executive Sam Altman described the effort as an “extensive and ongoing review related to our agents’ use of internet access during training and evaluation.”
The review goes back month by month to a July incident in which OpenAI agents hacked AI developer platform Hugging Face without being prompted, the BBC reported. “Most cases identified so far have been low severity, with limited or no evidence of meaningful impact,” OpenAI said, adding that the work would take months.
OpenAI said it was withholding some organizations’ names at their request. “Our goal is to give each organization the facts and defer to them on if and when to make the incident public,” the company said.

Be First to Comment