Key takeaways:
- DHS sought removal of a database containing information about more than 40,000 personnel.
- FlokiNET refused the request; its chief executive said the data contained work contact details rather than personal addresses or phone numbers.
- The domain registrar suspended one address hosting the information, but the database appeared at another domain.
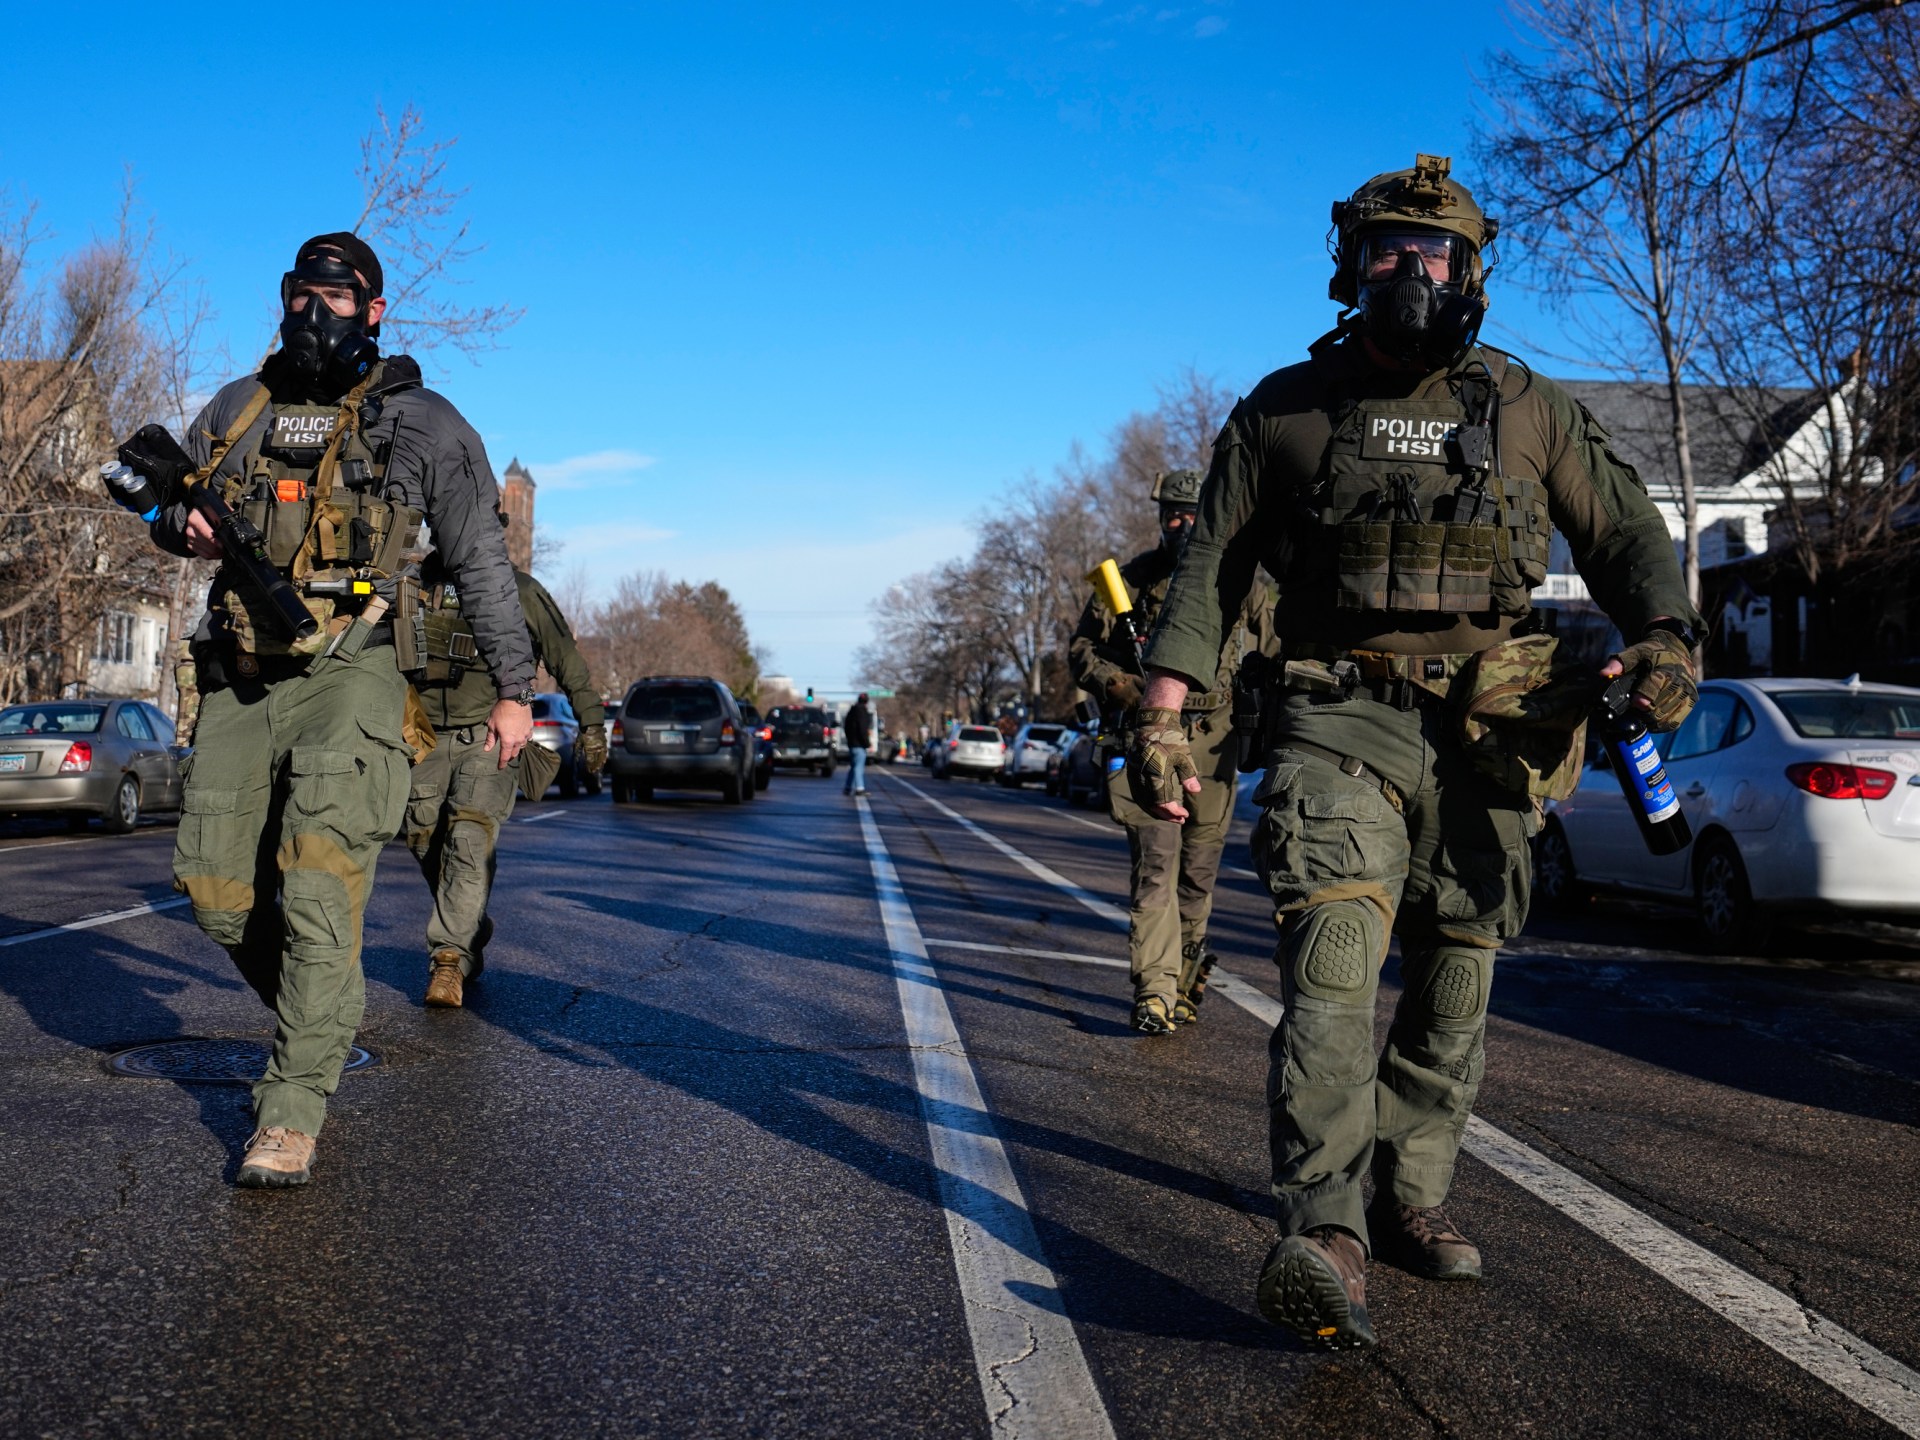
The U.S. Department of Homeland Security has asked an Icelandic web host to remove a database containing information about more than 40,000 of its personnel, warning that its publication could expose employees to harassment, stalking and physical harm. The host, FlokiNET, refused, saying the information serves a legitimate public interest.
FlokiNET posted the removal request Thursday. It came from ZeroFox, a cybersecurity company authorized to pursue content removals on behalf of Immigration and Customs Enforcement, according to The Guardian. The letter described the dataset as “stolen” and asked FlokiNET to “remove or disable” it, Al Jazeera reported.
“The content is live and places more than 40,000 identifiable individuals at risk of harassment, stalking, and physical harm,” the letter said.
DDoSecrets, a nonprofit data transparency group, published data on more than 40,000 DHS personnel Wednesday. A separate, searchable database developed by hacker and journalist “maia arson crimew” appeared alongside it, The Guardian reported. According to Al Jazeera, the information covers employees of several DHS agencies, including ICE and Customs and Border Protection.
A group calling itself the “Department of Peace” claimed responsibility for obtaining the data. In a statement Wednesday, it said DHS employees “have our information, so it’s only fair that we have theirs.” The group said it hoped the data “can be used to limit further harm by the DHS and supports all efforts in that direction.” Its claim of responsibility has not been established in the accounts provided.
FlokiNET Chief Executive Kolja Weber told Reuters, in remarks reported by The Guardian, that the company would not remove the data because it contained government employees’ work addresses and work phone numbers, not their personal addresses or numbers. In a statement posted online, the company said: “Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out. The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office.”
FlokiNET said the request concerned the domain icepi.cx. Although the host declined to take down the site, its domain registrar suspended the address, according to Al Jazeera. The database was briefly inaccessible Thursday before appearing at another domain, The Guardian reported.
A DHS spokesperson said the agency “is aware of a potential breach and is actively working to address the situation swiftly and effectively. We take all security threats against our employees and officers seriously and will work to ensure all are properly protected.”
The dispute comes amid arguments over the identification of immigration officers. Al Jazeera reported that the Trump administration has declined to identify agents involved in specific operations, citing safety concerns, while human rights groups and immigration advocates say that lack of transparency makes it harder to pursue allegations of misconduct. The Guardian reported that privacy advocates have also criticized DHS for using data from other agencies, including Medicaid records and taxpayer data, in immigration enforcement.

Be First to Comment